

While industry participants such as Tether and Circle are taking steps to freeze billions of dollars in assets, attackers are racing against time to convert the stolen stablecoins into cryptocurrencies that the issuers cannot freeze.
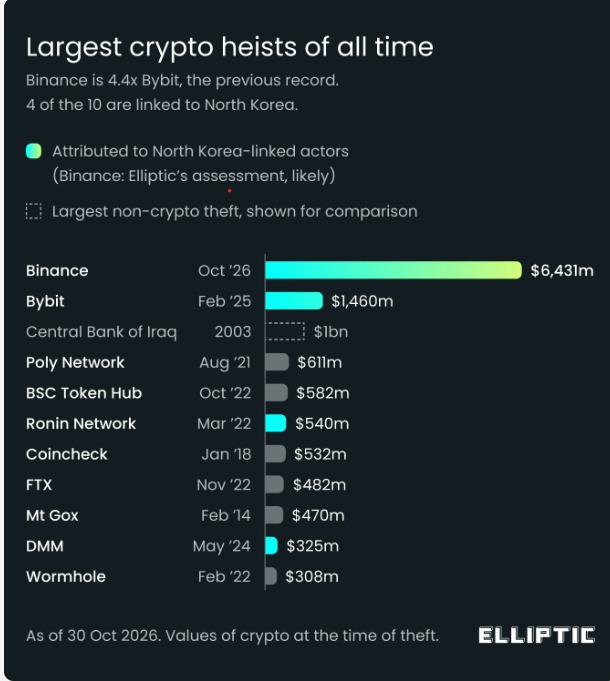
It is estimated that the scale of this hacker attack on Binance amounts to $6.3 billion. Although the token issuer has attempted to freeze the stolen funds, the attackers still control billions of dollars in stolen cryptocurrencies.
This attack is the largest in the history of the cryptocurrency industry, beginning at 20:04 UTC on Thursday. The perpetrators are believed to be linked to the same group of North Korean hackers behind the Bitget hacking incident last month, and they immediately began converting assets after succeeding.
The hackers' strategy is to convert assets that can be frozen, such as USDT and USDC, into assets that cannot be frozen, like Bitcoin (BTC) and Ethereum (ETH).
Engineer Dickson Wu traced that $500 million was sent to a certain address, of which $325 million was sold to market makers before 20:59 UTC in exchange for ETH. This occurred less than an hour after the start of the hacker attack.
They are racing against some of the most powerful “gatekeepers” in the crypto industry: Stablecoin giants such as Tether and Circle had already begun to blacklist addresses associated with theft at that time.
On Friday, Binance stated that out of the estimated total of $6.3 billion in stolen assets, about $3 billion has been frozen on the blockchain. The company is collaborating with law enforcement authorities, issuers, and blockchain analysis firms to track down more funds.
Even by the standards of the cryptocurrency industry, the scale of this theft is shocking. But with about half of the assets already frozen, how much of the stolen cryptocurrencies can the perpetrators possibly spend?
Cryptocurrencies with a "turn-off switch"
Unlike BTC or ETH, the latter two are decentralized cryptocurrencies that do not have a centralized issuer, and no one can press a pause button; however, for centralized stablecoins such as USDC issued by USDT and Circle issued by Tether, the issuers can freeze tokens held by specific addresses.
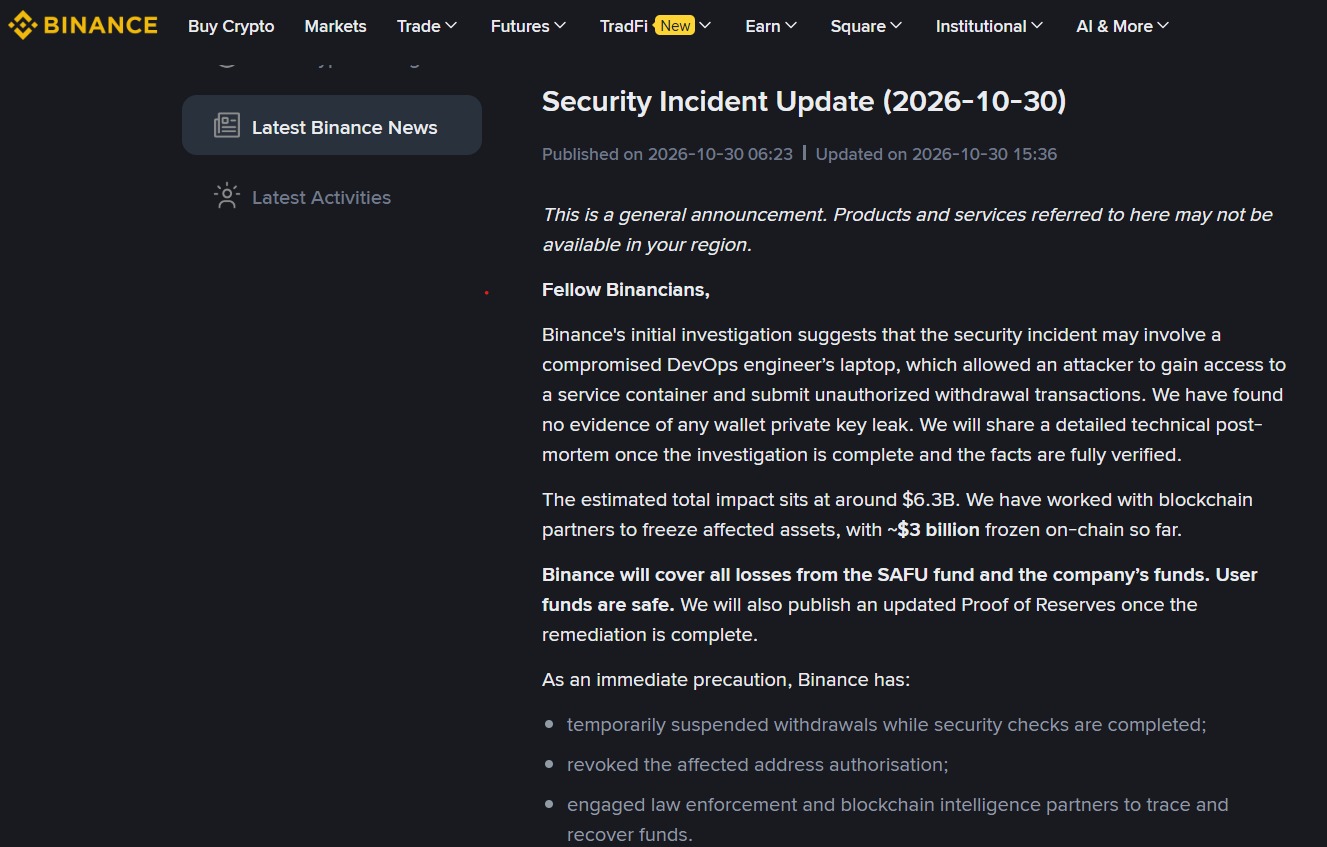
Binance stated that the company is cooperating with law enforcement authorities to trace the funds.
This enables them to take prompt action in such incidents. Tether has frozen a total of approximately $1.567 billion USDT, with the first large-scale freeze occurring just 37 minutes after the stolen funds entered the attackers' wallets, which were primarily Ethereum-based.
Three minutes later, Circle froze approximately $823 million in USDC, and other issuers such as Ripple and World Liberty Financial quickly followed suit.
The ability to render crypto assets immobile is not unique to stablecoins. Despite the absence of a centralized issuer, some decentralized protocols have not stood by idly either, such as Arbitrum.
The Security Committee has transferred approximately $30.5 million in ARB and ETH to an intermediate frozen wallet. These assets cannot be transferred until further action by the committee or until a governance vote on Arbitrum DAO is conducted.
However, there is still an important distinction: frozen funds do not necessarily equate to funds that have been recovered. Making assets immobile can prevent suspected attackers from spending that money, but it does not automatically return the funds to Binance or its users.
The complexity brought about by Aave
Decentralized lending protocol Aave has added another layer of complexity to the situation. Between 20:58 and 21:01 UTC, a wallet associated with the attacker deposited 60 million US dollars USDT into the Aave V3 on Ethereum and lent out 44.6 million US dollars in wrapped Ether (WETH); this occurred about 40 minutes before the first freeze.
LlamaRisk is a Aave risk service provider. In an update at 1:00 a.m., the institution stated that the attacker subsequently held approximately $59.9 million in USDT collateral, corresponding to $43.8 million in debt. Aave indicated that this position is still in a state of overcollateralization and will not pose a risk to the providers of protocol funds.
Since USDT has already been deposited into the lending pool of Aave, blacklisting the attacker's wallet does not automatically retrieve the collateral held by the protocol. As explained by Aave Chan Initiative founder Marc Zeller:
“USDT is a real currency backed by the US dollar, and from the perspective of the protocol, although this position involves criminal activities, it is still considered overcollateralized.”
To prevent further deposits and loans, Aave has temporarily frozen its various markets deployed under V3 and V4. However, existing users can still withdraw funds, repay loans, and liquidate their positions.
Aave subsequently lifted the preventive freezes on the V3 and V4 markets, stating that their contracts were not affected, and that the related positions still maintained excess collateral.
"It's just an ordinary day in the crypto industry," said Zeller.
So, what exactly can attackers still retain?
As of 7:00 a.m. on Friday, it is estimated that $2.84 billion has been frozen, while attackers still control approximately $3.33 billion in assets that the issuer is unable to freeze.
Although the freezing measures have almost halved the pool of funds that attackers can profit from, this does not necessarily mean that the remaining funds can be safely recovered.
Bitcoin and Ethereum do not have centralized token issuers that can blacklist individual addresses like Tether or Circle. Therefore, while transactions may be restricted once stolen assets are converted into these native cryptocurrencies, it is much more difficult to freeze them.
Binance has pledged to use its user security asset fund (SAFU) and company funds to cover all losses, and stated that user assets remain safe. According to the latest update from Binance CEO Richard Teng, the exchange is already "recovering stolen assets for users."