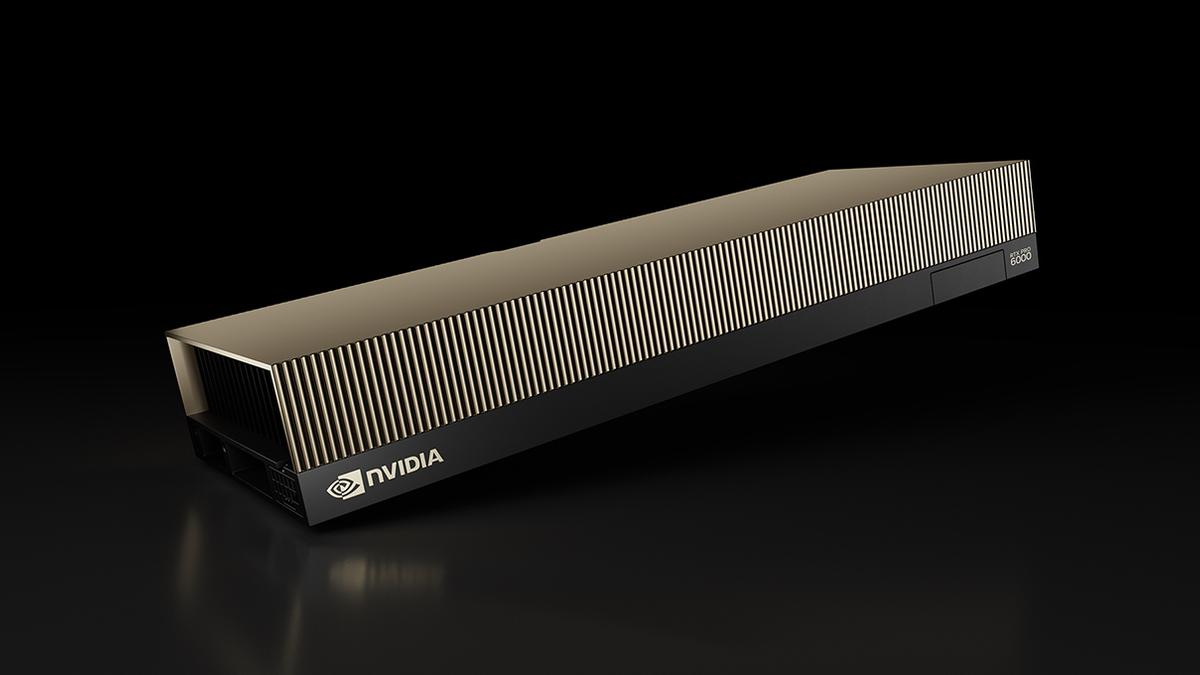


Enterprises are willing to deploy their models on the cloud, but they may not be willing to expose their training materials, customer inputs, or model weights during the infrastructure management process. On October 21st, Google Cloud announced that Confidential G4 equipped with NVIDIA RTX PRO version 6000 of Blackwell Server GPU has moved from preview to general availability, covering 36 availability zones and can be used on Compute Engine virtual machines and GKE nodes. The key point of this news is not just that there is another GPU, but rather that confidential computing is beginning to make its way into the regular procurement lists for enterprises' high-intensity AI workloads. However, general availability does not mean that any AI tasks automatically enjoy end-to-end confidentiality; the security outcome still depends on the configuration, certifications, and the applications themselves.
Which segment of risk is addressed by hardware protection?
Google emphasizes in the official documentation that Confidential G4 combines hardware-supported memory encryption, non-exportable hardware keys, and verifiable remote proofs to attempt to protect data in operation as well as model parameters. Traditional data encryption typically covers storage and transmission, but when actual computation begins, data has to enter memory. What confidential computing aims to reduce is precisely this exposed area: it allows workloads to run in a hardware-constrained execution environment while providing proof of the environmental state to the caller. For companies that host proprietary model weights in the cloud or process sensitive customer materials, this is more relevant than simply encrypting disks.
However, "proving the environment is credible" is not the same as "proving that the business logic is correct." Remote verification can assist in confirming that programs run on the expected hardware and configurations, but it cannot replace input validation or model output checks, nor can it automatically detect flaws in application logic. Enterprises still need to clarify who issues the certification materials, how the verifiers conduct inspections, whether the certification changes after image and driver updates, and under what conditions keys are delivered to workloads. If verification steps remain at the supplier demonstration stage and are not integrated into deployment and troubleshooting processes, hardware capabilities will hardly become a true control measure.
Google It should also be noted that Confidential Space's support for secure multi-party data sharing will gradually become generally available in the coming weeks. This is not the same status of availability as Confidential G4 instances, which are already generally available. Describing both as 'all confidential data collaboration functions are now fully online' could mislead teams preparing to design cross-institutional workflows. Whether an application can utilize these capabilities also depends on the region, instance specifications, GKE configuration, and specific service limitations, rather than assuming that every combination can be deployed immediately just because there are '36 availability zones'.
What enterprises need to verify is not just the concept of "zero trust."
Only after incorporating GPU into confidential computing does the economic viability of the product begin to be truly tested by actual business operations. The security team is concerned about data exposure during use, the engineering team focuses on throughput, latency, driver compatibility, and operational complexity, while the finance team looks at the total cost of each task. Google mentions in the announcement positive customer feedback regarding deployment experience and performance, but these are specific cases and should not be taken as a general result for all models or all batch tasks. Especially in scenarios involving multi-card training, complex network communications, and frequent loading of weights, enterprises need to compare their own images, data scales, and performance baselines.
Actual pilots can start with three key questions. First, which sensitive data needs to be protected during runtime, and does the risk come from cloud administrators, the hosting environment, or the application's own call chain? If the main risk of leakage is due to end-users accidentally transmitting data or proxies sending content to third-party tools, then protecting only the GPU memory is not sufficient. Second, are the startup, scaling, upgrading, and rollback of workloads all included in the proof and key management policies? Third, can the evidence obtained by auditors link a real business task with a verifiable hardware state, rather than just seeing a product promotional image?
The market significance also lies in the reduction of procurement barriers. In the past, confidential GPU projects were often considered to be highly customized; now that they are generally available, they have been incorporated into the support, billing, and operations systems of standard cloud products. As a result, it has become easier for companies to include privacy protection in their regular architectural reviews, without having to create a separate computing environment for sensitive projects at the last minute. However, "easier deployment" does not equate to "no need for governance": overly broad permissions, log leaks, external tool calls, and residual data on the output side can all potentially bypass the protected computing areas.
Google This release has indeed taken confidential computing a step forward towards large-scale AI services, but it's important to clarify the boundaries: Confidential G4 instances are now generally available, while Confidential Space related support is still being gradually rolled out. The most prudent way to assess this is not to ask whether it is absolutely secure, but to choose a real but controllable sensitive workflow and record whether the hardware proof can be independently verified, whether the performance and cost are acceptable, and whether it can safely degrade in case of failure. Only when these indicators are met can the new capabilities at the hardware level be considered as productive capabilities that enterprises dare to rely on.
It is also necessary to consider the whereabouts of data outside the protected scope. A single inference task may involve putting prompt words into a queue, writing intermediate states to temporary files, and then handing over the results to logs, monitoring systems, and downstream plugins; not all of these steps are necessarily executed within the same confidentiality boundaries. When designing a pilot project, it is essential to draw a complete data flow diagram that includes input, computation, output, and backup, and to clearly indicate who has access to each part of the data, for how long it can be stored, and how it should be deleted. Only by aligning the hardware specifications with this data flow diagram can purchasers be sure of the level of protection they are actually obtaining, rather than mistaking a product name for a commitment to protect the entire system's privacy.